Hello,
If you know some gov or some company domain, its likely that many vulnerable or non non vulnerable targets will be registered under the same subnet (usually a /24 is enough)
You just need to specify the ports or the services detection method and nmap will do the job.
You need the "whois" command installed in your system to know more details about the domains and who is managing them ..
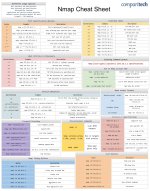
So this is a cheatsheet I liked to share as a first step into this shit. (attached)
Dont use it for bad stuff.
Thanks
If you know some gov or some company domain, its likely that many vulnerable or non non vulnerable targets will be registered under the same subnet (usually a /24 is enough)
You just need to specify the ports or the services detection method and nmap will do the job.
You need the "whois" command installed in your system to know more details about the domains and who is managing them ..
So this is a cheatsheet I liked to share as a first step into this shit. (attached)
Dont use it for bad stuff.
Thanks